Sequentia Explores: The Mathematics of Crypto
Part VI: Building a Blockchain – The Math of a Distributed Ledger
Lecture 39: Proof-of-Work: The Math of Making Tampering Expensive
In our last few lectures, we’ve built the structure of a blockchain. We’ve seen how individual transactions are authorized with digital signatures, bundled into blocks summarized by a Merkle Root, and chained together chronologically using the hash of the previous block.
We’ve established that this chain of hashes makes the ledger tamper-evident. If an attacker changes a past block, the hash of that block changes, breaking the chain. To successfully rewrite history, the attacker would have to re-calculate the hash for that block and every single block that follows it.
This raises a critical question: what stops them from just doing that? If calculating a SHA-256 hash is lightning fast for a computer, why can’t an attacker just alter a block and recalculate all the subsequent hashes in a few seconds?
The answer lies in the ingenious mechanism that deliberately makes the process of “sealing” a block incredibly difficult, time-consuming, and expensive. This mechanism is called Proof-of-Work (PoW).
What is Proof-of-Work?
As we first explored in Lecture 35, Proof-of-Work is a system that requires a significant but feasible amount of computational effort (the “work”) to be expended in order to produce a piece of data. The key is that this “work” must be hard to do, but easy for others to verify.
In Bitcoin, the “work” is the process of solving the hash puzzle: repeatedly hashing the block header with a different nonce until the resulting hash is below a specific target value (i.e., starts with a required number of zeroes).
The Economic and Computational Security Model
Proof-of-Work isn’t just a fun puzzle; it’s the economic and computational security model that protects the entire blockchain. It transforms the abstract concept of a “tamper-evident” chain into a tamper-resistant and prohibitively expensive one.
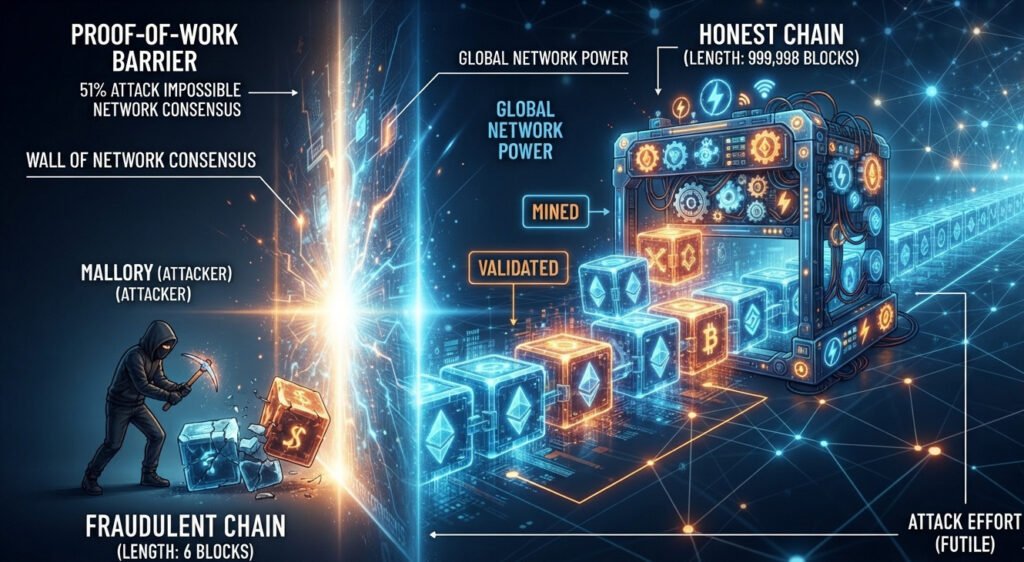
Let’s revisit our attacker, Mallory, who wants to alter a transaction in Block 50. We know she has to re-calculate the hash for Block 50 and all subsequent blocks. With Proof-of-Work, this means she has to:
- Alter the transaction in Block 50.
- Re-do the Proof-of-Work for Block 50: She must start the brute-force guessing game, trying trillions of nonces until she finds a new “golden hash” for her altered Block 50. This process is designed by the Bitcoin network to take, on average, 10 minutes for the entire global network combined. Mallory must do this alone.
- Re-do the Proof-of-Work for Block 51: Once she’s mined her fraudulent Block 50, she must take its new hash, place it in Block 51, and start the mining process all over again for Block 51.
- Repeat for every block… all the way to the present.
The Unwinnable Race Against Time
Here’s the crucial part: while Mallory is frantically trying to re-mine the history of the blockchain, the rest of the honest network is still moving forward.
Every 10 minutes, on average, the honest network finds a new block and adds it to the legitimate chain, making that chain even longer.
Mallory is not just in a race to re-do past work; she is in a race against the combined computational power of the entire honest network. To successfully pull off her attack and have her fraudulent chain accepted as the new “truth,” she would need to start at Block 50, re-mine all the blocks up to the present, and then overtake the honest chain.
This requires a “51% Attack.” To have a probabilistic chance of succeeding, Mallory would need to control more than 50% of the total hashing power of the entire global network. Acquiring and operating this amount of specialized hardware (ASICs) and the electricity to run it would cost billions of dollars, making it an economically irrational and practically impossible feat for any single attacker.
“Work” as a Proxy for Trust
In a decentralized system with no central authority, how do you decide which version of the ledger is the correct one? Proof-of-Work provides an elegant answer: the longest chain is the truth.
Why? Because the longest chain is the one that has had the most computational work, the most energy, and the most time invested in it. It represents the consensus of the majority of the network’s power. Any attempt to create a fraudulent chain would require an infeasible amount of work to catch up, let alone overtake, the accumulated work of the honest chain.
Proof-of-Work brilliantly converts the abstract concept of “effort” into a verifiable, mathematical property of the data. It makes the history of the ledger not just a sequence of data, but a sequence of costly and time-consuming computational achievements. Tampering with the past isn’t just a matter of changing a file; it’s a matter of trying to single-handedly re-run a significant portion of the network’s entire computational history.
This is why the blockchain is considered immutable. Not because the data can’t physically be changed, but because the economic and computational cost required to do so is so astronomically high that it is, for all practical purposes, impossible.
